
Adding Secrets
Secrets can be created at group or user scope. A secret holds the credentials needed to access resources such as containers in a private OCI registry or input files stored in an S3 bucket.
SIF image decryption secrets can currently only be created using the CLI.
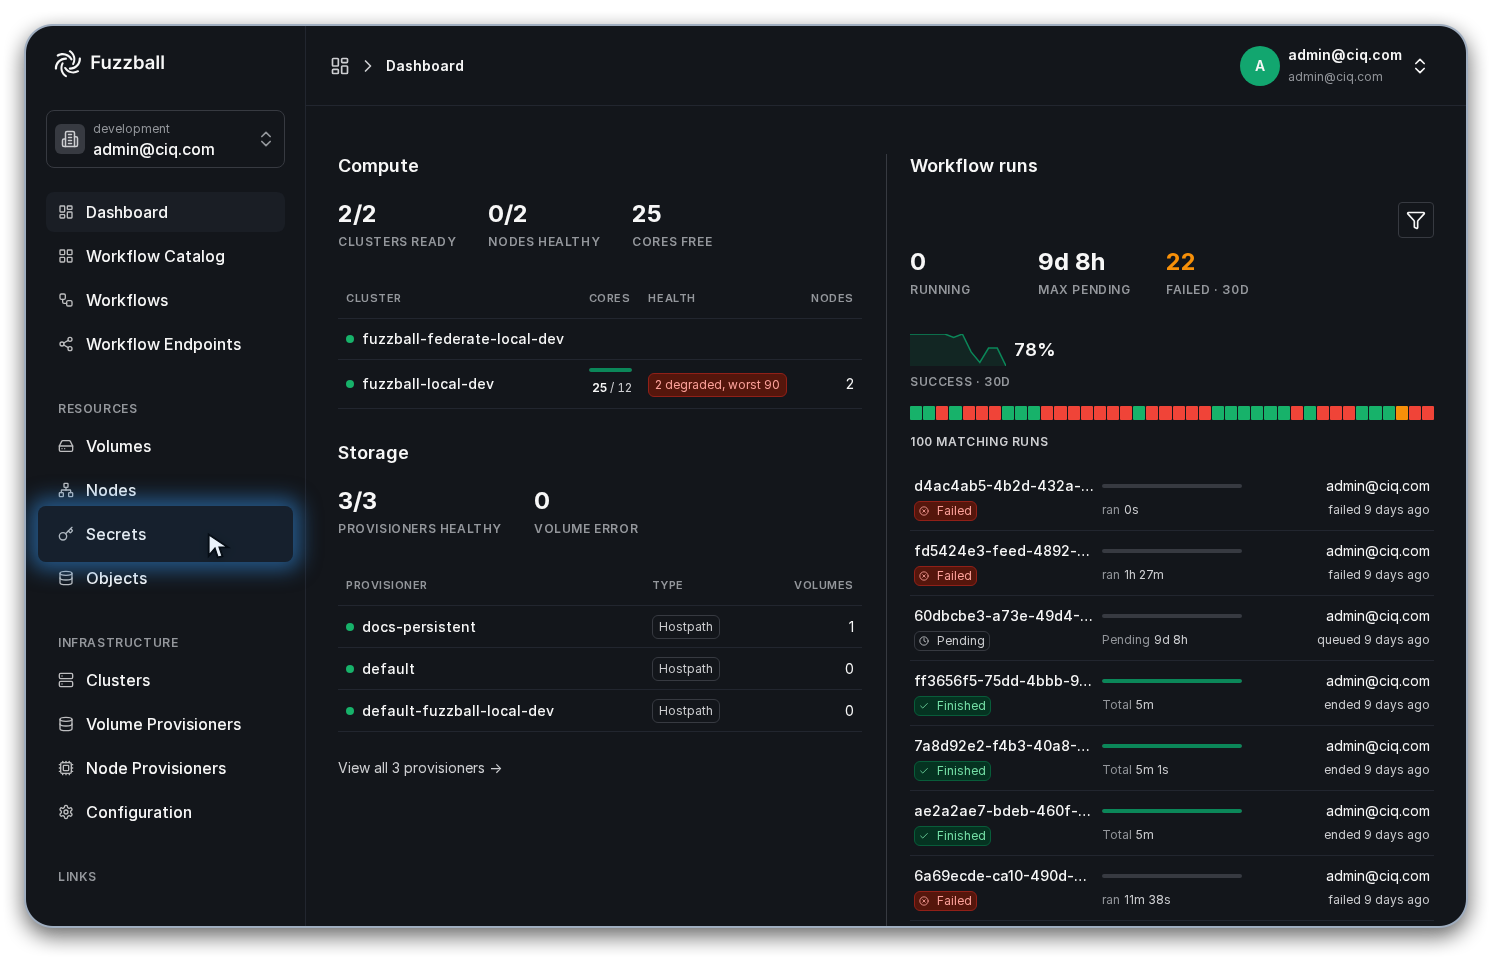
Once you have logged in and selected one of your groups, you can create a secret by first navigating to the secrets page using the navigation bar on the left side of the page. The image below shows a user logged in with a group selected.
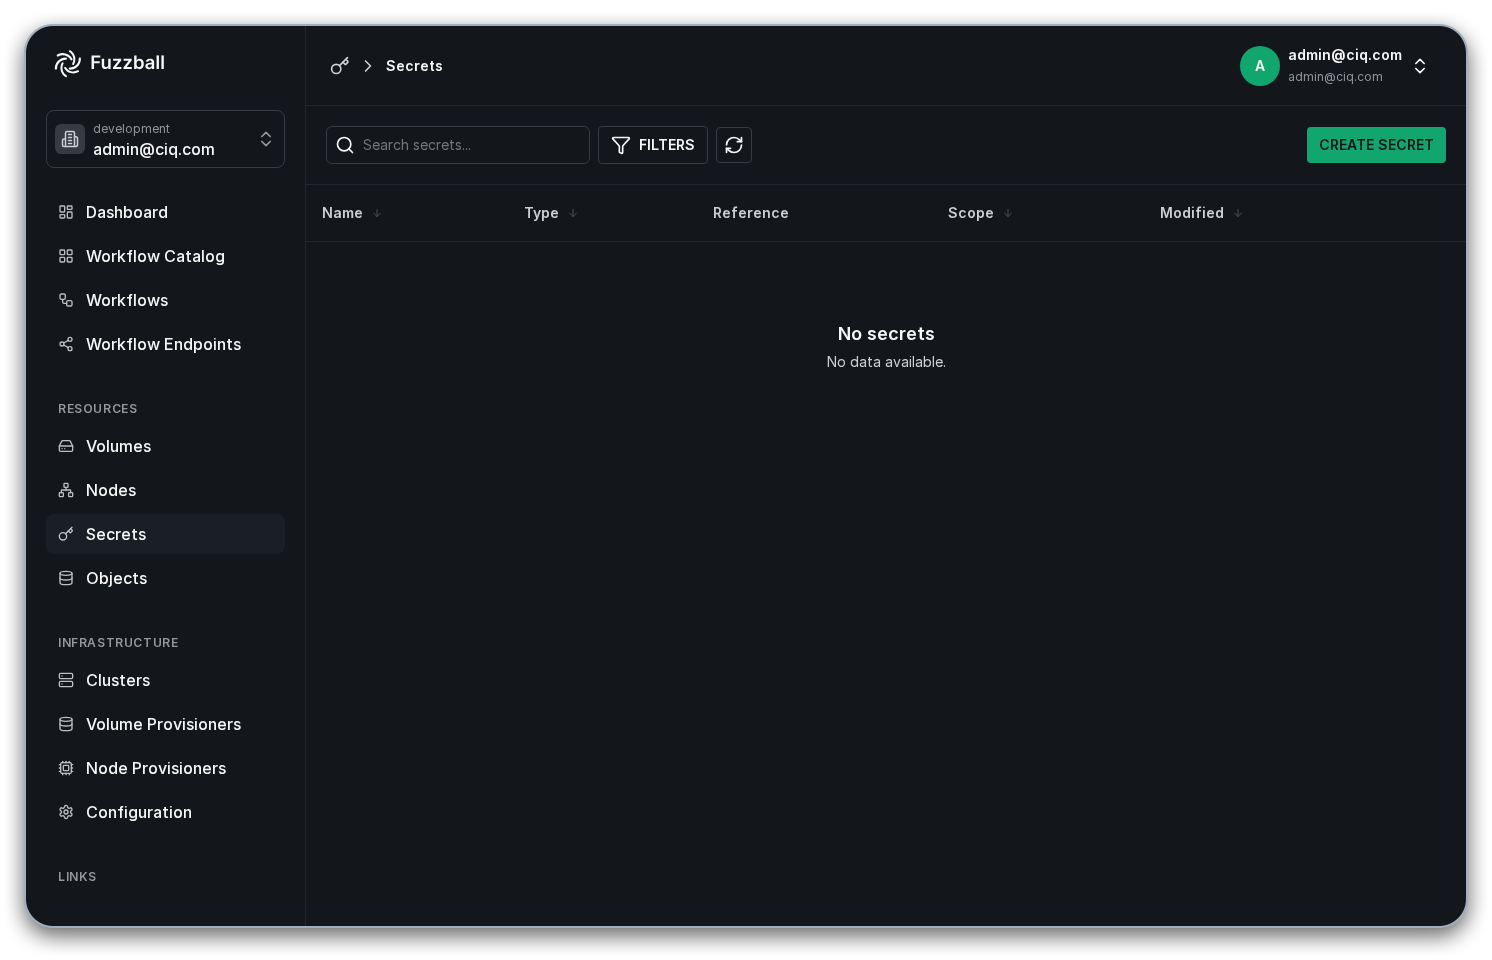
Navigating to the secrets page shows a list of group and user scoped secrets you have access to. In the example below no secrets have been created yet. Let’s add one now by clicking the “Create Secret” button in the top right.
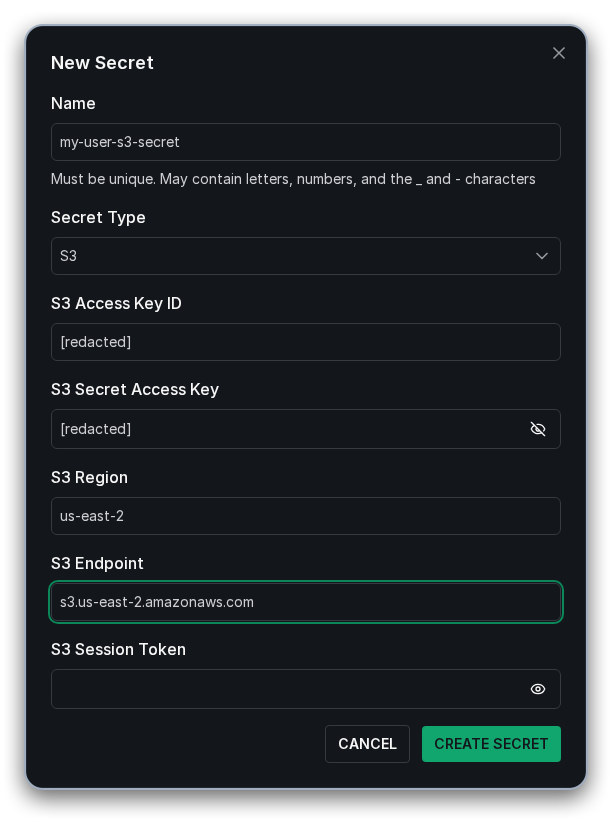
Fuzzball enables you to create secrets at the user or group scope. When you are working in a group
account, a Scope selector appears at the top of the dialog so you can choose between User and
Group (account owners) or Organization (organization owners). When you are working in your
personal account there is nothing to choose – every secret is user scoped – so the selector is
omitted, as in the image below. Next, you can give your secret a name and select the type of secret
you’d like to create. In the example
below, the secret being created is named my-user-s3-secret and its type is set to S3 using the
drop down. The dialog renders the fields that type requires. In the example below the fields are
access key ID, secret access key, region, and endpoint. Session token is optional: supply it
only when authenticating with a temporary Amazon Web Services (AWS) Security Token Service
credential. Once the required fields are filled in, click Create Secret at the bottom right
of the dialog.
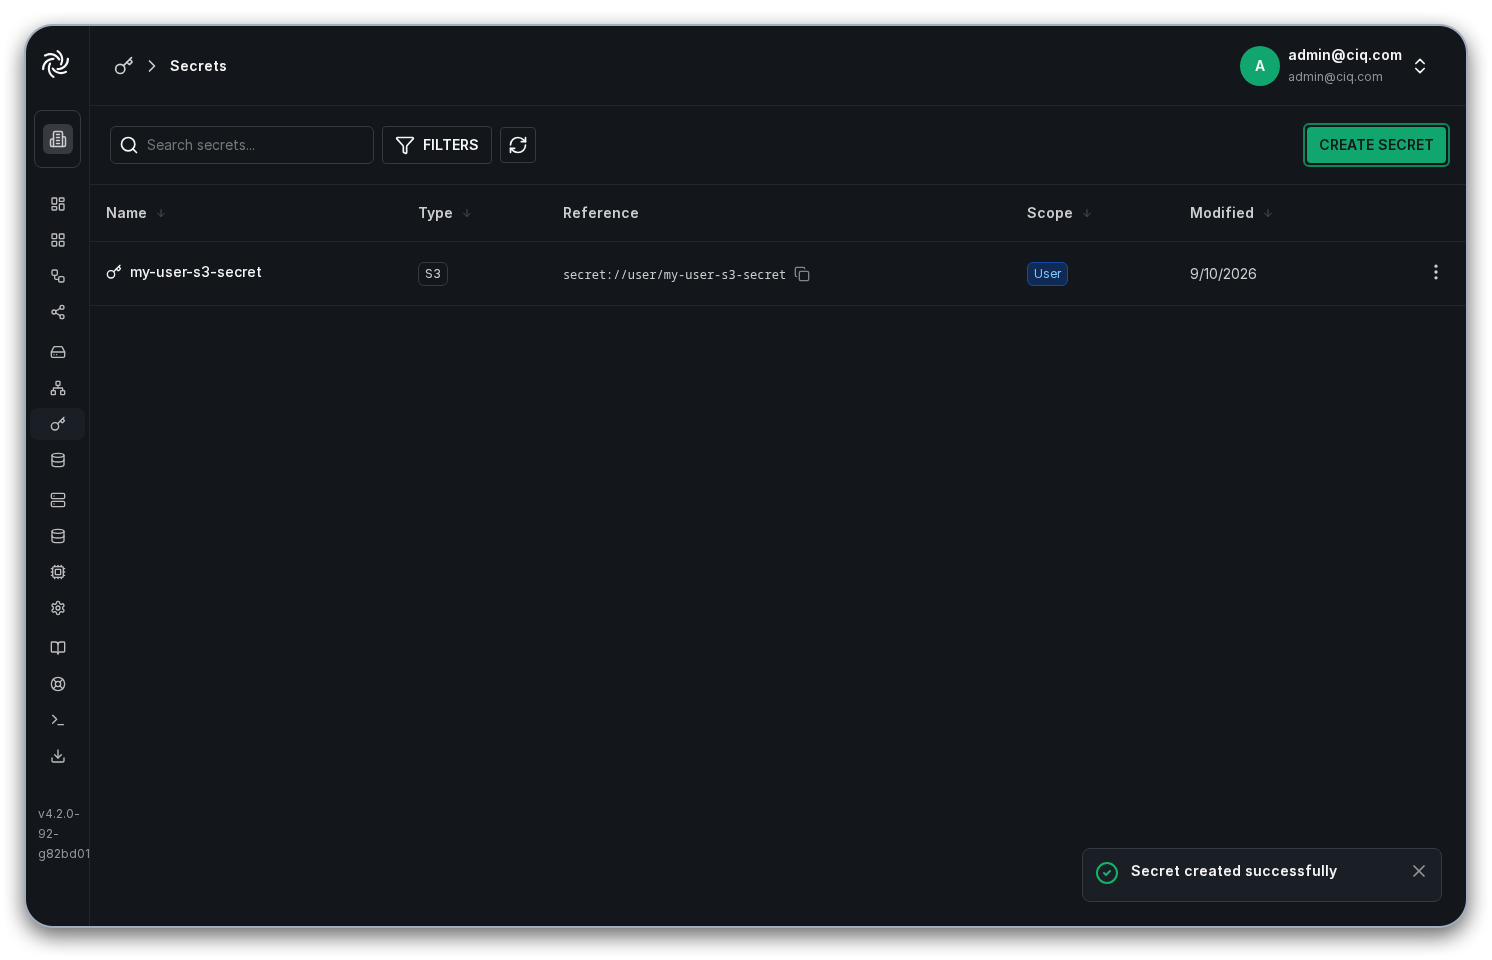
In this example, after the S3 secret my-user-s3-secret is created, it is appended to the list of
secrets you have access to.
Once you have created an appropriate secret YAML file, adding the secret to the cluster can be done like so:
$ cat > s3-secret.yaml <<__EOF__
type: s3
secret:
  access-key-id: "[redacted]"
  access-key: "[redacted]"
  region: us-east-2
  endpoint: s3.us-east-2.amazonaws.com
  session-token:
__EOF__

$ fuzzball secret create my-user-s3-secret s3-secret.yaml --from-file -s user
Created secret: 304945fc-e915-4359-8adc-1f59d3c1de92

$ fuzzball secret list
ID                                   | TYPE | REFERENCE
304945fc-e915-4359-8adc-1f59d3c1de92   s3     secret://user/my-user-s3-secret
To add a secret with group scope instead of user scope, and assuming you have permission to do
so, change -s user to -s group (the legacy value -s account is also accepted and behaves
identically):
$ fuzzball secret create my-group-s3-secret s3-secret.yaml --from-file -s group
Created secret: f0bea820-c2a2-4a2f-b738-649f8a494150

$ fuzzball secret list
ID                                   | TYPE | REFERENCE
304945fc-e915-4359-8adc-1f59d3c1de92   s3     secret://user/my-user-s3-secret
f0bea820-c2a2-4a2f-b738-649f8a494150   s3     secret://group/my-group-s3-secret
Creating a group scoped secret requires the correct group to be selected. If your currently selected group is your individual group, Fuzzball adds the secret to your personal user scope even when you pass-s group. Usefuzzball group listto see which group is selected, andfuzzball group selectto change it.